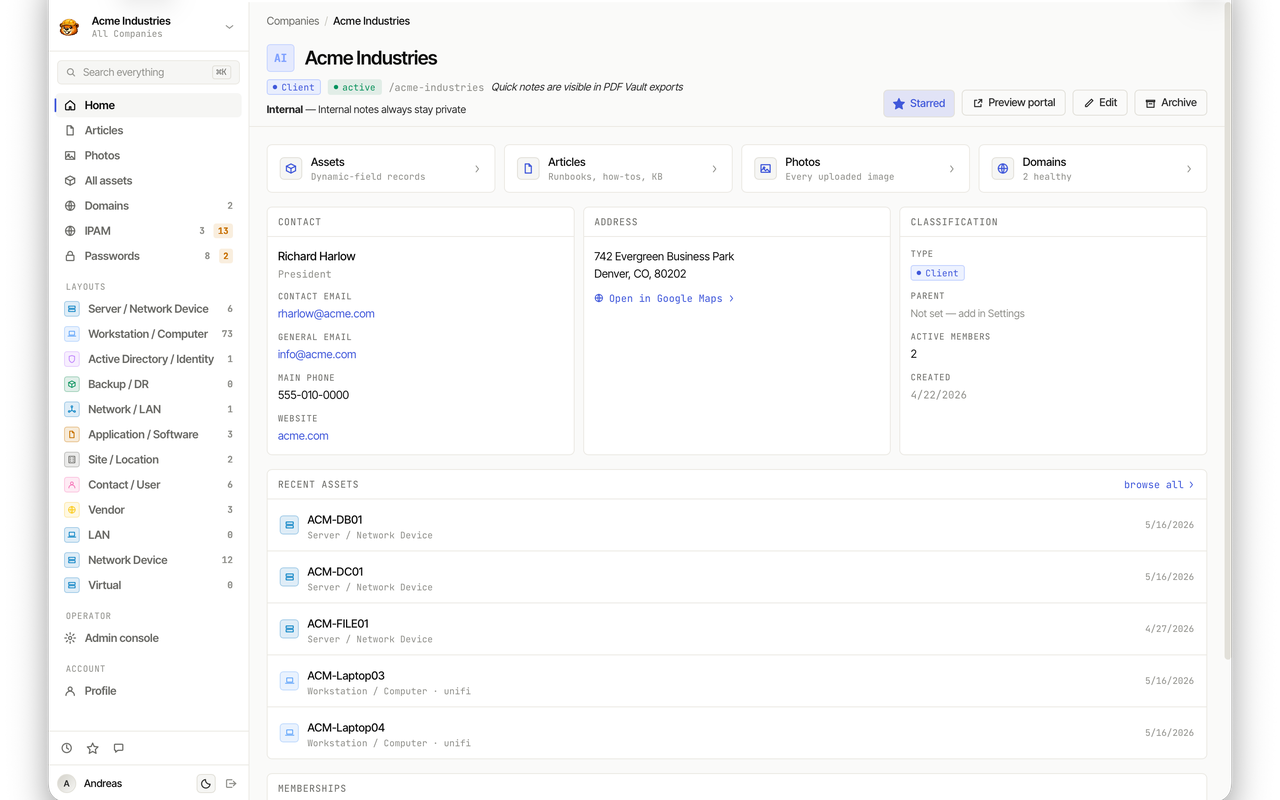
Open-source, self-hosted IT documentation and asset management platform built around a relational knowledge model.
Parts
Service
Image
Role
postgres ghcr.io/daemonless/postgres:16docs
redis ghcr.io/daemonless/redis:latestdocs
api ghcr.io/daemonless/weavestream-api:latestdocs
worker ghcr.io/daemonless/weavestream-worker:latestdocs
web ghcr.io/daemonless/weavestream-web:latestdocs
Before deploying, ensure your host environment is ready. See the Quick Start Guide for host setup instructions, including the security model for host vs. container privileges.
Deployment
1. Save as .env and fill in what is empty:
1000
1000
UTC
2. Save as compose.yaml:
name : weavestream
services :
postgres :
image : ghcr.io/daemonless/postgres:16
container_name : weavestream-postgres
restart : always
annotations :
org.freebsd.jail.allow.sysvipc : "true"
environment :
POSTGRES_USER : ${POSTGRES_USER:-weavestream}
POSTGRES_PASSWORD : ${POSTGRES_PASSWORD:-weavestream}
POSTGRES_DB : ${POSTGRES_DB:-weavestream}
PUID : ${PUID:-1000}
PGID : ${PGID:-1000}
TZ : ${TZ:-UTC}
volumes :
- ${DATA_DIR}/postgres:/var/lib/postgresql/data
redis :
image : ghcr.io/daemonless/redis:latest
container_name : weavestream-redis
restart : always
environment :
PUID : ${PUID:-1000}
PGID : ${PGID:-1000}
TZ : ${TZ:-UTC}
volumes :
- ${DATA_DIR}/redis:/config
api :
image : ghcr.io/daemonless/weavestream-api:latest
container_name : weavestream-api
restart : always
depends_on :
- postgres
- redis
environment :
PUID : ${PUID:-1000}
PGID : ${PGID:-1000}
TZ : ${TZ:-UTC}
DATABASE_URL : postgresql://${POSTGRES_USER:-weavestream}:${POSTGRES_PASSWORD:-weavestream}@postgres:5432/${POSTGRES_DB:-weavestream}
REDIS_URL : redis://redis:6379/0
APP_URL : ${APP_URL:-http://localhost:3000}
API_URL : ${API_URL:-http://localhost:3000/api}
FILE_STORAGE_DIR : /var/lib/weavestream/files
BACKUP_STORAGE_DIR : /var/lib/weavestream/backup
JWT_SIGNING_KEY : ${JWT_SIGNING_KEY}
MFA_ENCRYPTION_KEY : ${MFA_ENCRYPTION_KEY}
PASSWORD_ENCRYPTION_KEY : ${PASSWORD_ENCRYPTION_KEY}
INTEGRATION_SECRET_KEY : ${INTEGRATION_SECRET_KEY}
SMTP_SECRET_KEY : ${SMTP_SECRET_KEY}
COOKIE_SIGNING_KEY : ${COOKIE_SIGNING_KEY}
CSRF_SIGNING_KEY : ${CSRF_SIGNING_KEY}
volumes :
- ${DATA_DIR}/files:/var/lib/weavestream/files
- ${DATA_DIR}/backup:/var/lib/weavestream/backup:ro
worker :
image : ghcr.io/daemonless/weavestream-worker:latest
container_name : weavestream-worker
restart : always
depends_on :
- redis
- api
environment :
PUID : ${PUID:-1000}
PGID : ${PGID:-1000}
TZ : ${TZ:-UTC}
DATABASE_URL : postgresql://${POSTGRES_USER:-weavestream}:${POSTGRES_PASSWORD:-weavestream}@postgres:5432/${POSTGRES_DB:-weavestream}
REDIS_URL : redis://redis:6379/0
APP_URL : ${APP_URL:-http://localhost:3000}
API_URL : ${API_URL:-http://localhost:3000/api}
FILE_STORAGE_DIR : /var/lib/weavestream/files
BACKUP_STORAGE_DIR : /var/lib/weavestream/backup
JWT_SIGNING_KEY : ${JWT_SIGNING_KEY}
MFA_ENCRYPTION_KEY : ${MFA_ENCRYPTION_KEY}
PASSWORD_ENCRYPTION_KEY : ${PASSWORD_ENCRYPTION_KEY}
INTEGRATION_SECRET_KEY : ${INTEGRATION_SECRET_KEY}
SMTP_SECRET_KEY : ${SMTP_SECRET_KEY}
COOKIE_SIGNING_KEY : ${COOKIE_SIGNING_KEY}
CSRF_SIGNING_KEY : ${CSRF_SIGNING_KEY}
volumes :
- ${DATA_DIR}/files:/var/lib/weavestream/files
- ${DATA_DIR}/backup:/var/lib/weavestream/backup
web :
image : ghcr.io/daemonless/weavestream-web:latest
container_name : weavestream-web
restart : always
depends_on :
- api
environment :
PUID : ${PUID:-1000}
PGID : ${PGID:-1000}
TZ : ${TZ:-UTC}
API_INTERNAL_URL : http://api:4000
COOKIE_SIGNING_KEY : ${COOKIE_SIGNING_KEY}
TRUST_PROXY_HOPS : ${TRUST_PROXY_HOPS:-1}
ports :
- "${WEB_HOST_PORT:-3000}:3000"
Then run podman-compose up -d.
Interactive Configuration
Parameters
Environment Variables
Variable
Default
Description
POSTGRES_USERweavestreamPostgreSQL database user (default: weavestream)
POSTGRES_PASSWORDweavestreamPassword for the PostgreSQL database
POSTGRES_DBweavestreamPostgreSQL database name (default: weavestream)
PUID1000User ID for the container processes
PGID1000Group ID for the container processes
TZUTCTimezone for the containers
APP_URLhttp://localhost:3000Public URL where users access Weavestream (default: http://localhost:3000 )
API_URLhttp://localhost:3000/apiPublic URL of the API (default: http://localhost:3000/api )
DATA_DIR./dataHost path for persistent data (files, backups, database, redis)
WEB_HOST_PORT3000Published host port for the web UI (default: 3000)
TRUST_PROXY_HOPS1Reverse proxy hops in front of the web UI, 0 when exposed directly (default: 1)
JWT_SIGNING_KEY<JWT_SIGNING_KEY>32-byte base64 secret shared by api and worker
MFA_ENCRYPTION_KEY<MFA_ENCRYPTION_KEY>32-byte base64 secret shared by api and worker
PASSWORD_ENCRYPTION_KEY<PASSWORD_ENCRYPTION_KEY>32-byte base64 secret shared by api and worker
INTEGRATION_SECRET_KEY<INTEGRATION_SECRET_KEY>32-byte base64 secret shared by api and worker
SMTP_SECRET_KEY<SMTP_SECRET_KEY>32-byte base64 secret shared by api and worker
COOKIE_SIGNING_KEY<COOKIE_SIGNING_KEY>32-byte base64 secret shared by api and worker, and web
CSRF_SIGNING_KEY<CSRF_SIGNING_KEY>32-byte base64 secret shared by api and worker
Volumes
Path
Description
/var/lib/postgresql/dataPostgreSQL database storage
Implementation Details
Architectures: amd64User: bsd (UID/GID set via PUID/PGID ). Defaults to 1000:1000.Base: Built on ghcr.io/daemonless /basesysvipc: Requires --annotation 'org.freebsd.jail.allow.sysvipc=true' (ocijail 0.5.0+ )
Need help? Join our Discord community.
 Weavestream