
daemonless
The native container platform for FreeBSD. Run 146+ modern apps with standard OCI tooling.
Production-grade images, automated builds, native performance.
What is Daemonless?
Daemonless is a collection of FreeBSD-native OCI images that run directly on the FreeBSD kernel. It combines the power and security of Jails with the modern container ecosystem—compatible with Podman, AppJail, fjord, Sylve, FreeCORE, or any OCI-compliant runtime. No Linux virtual machines or overhead required.
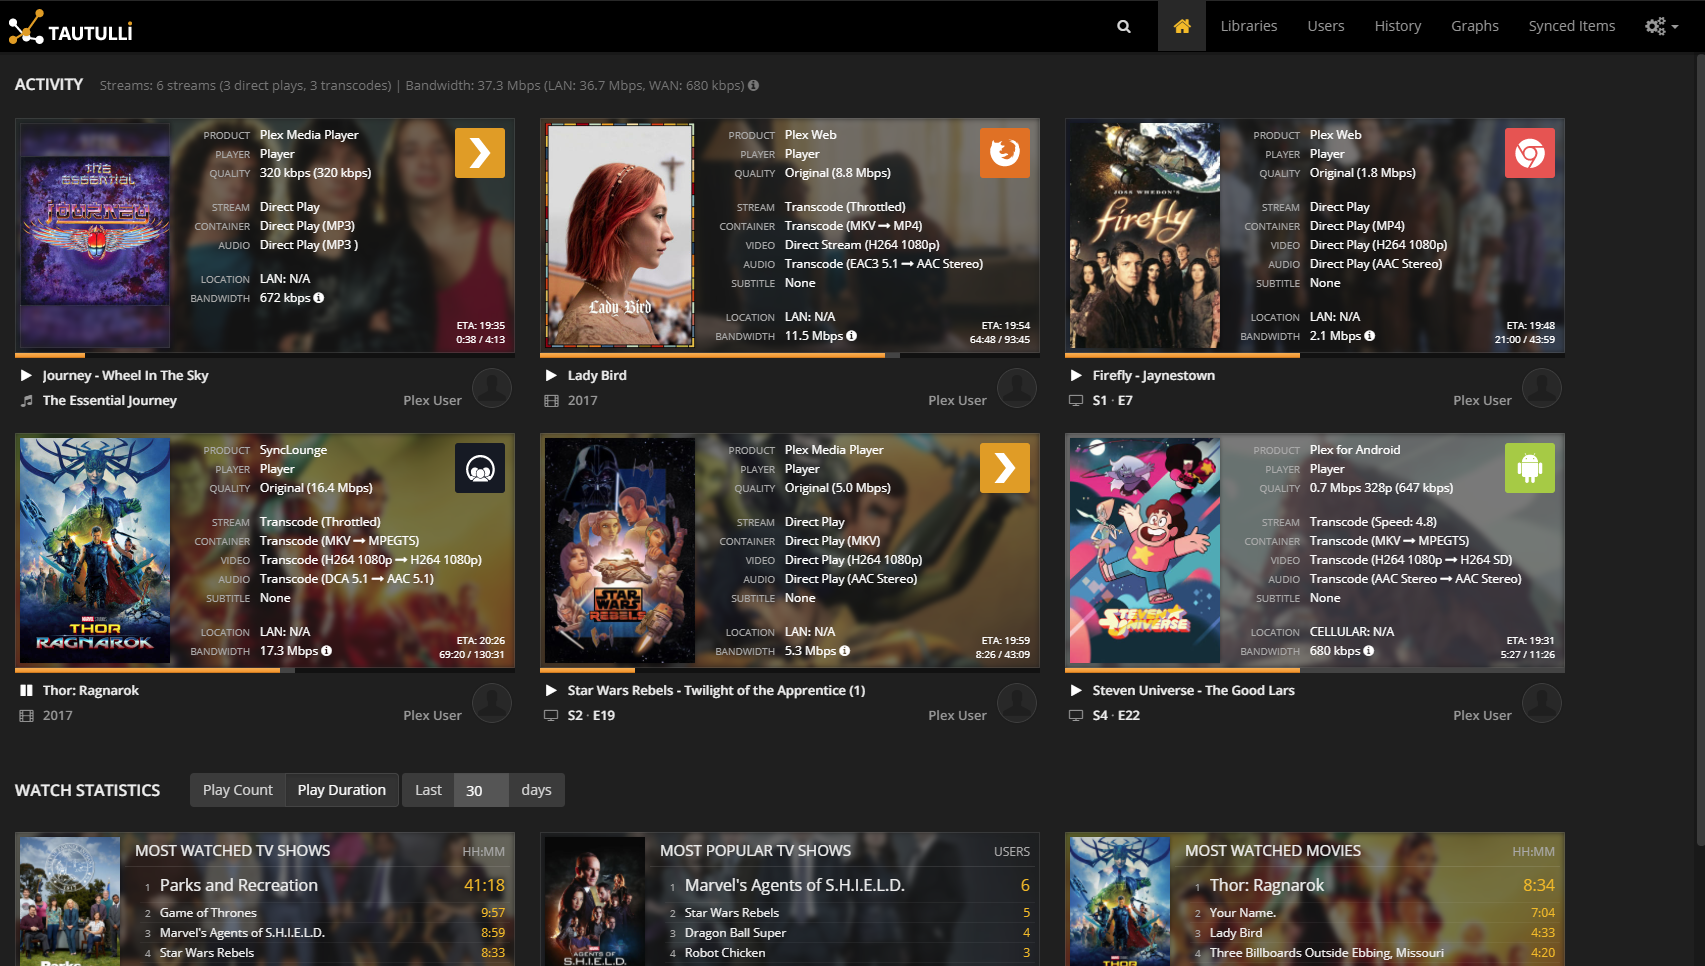
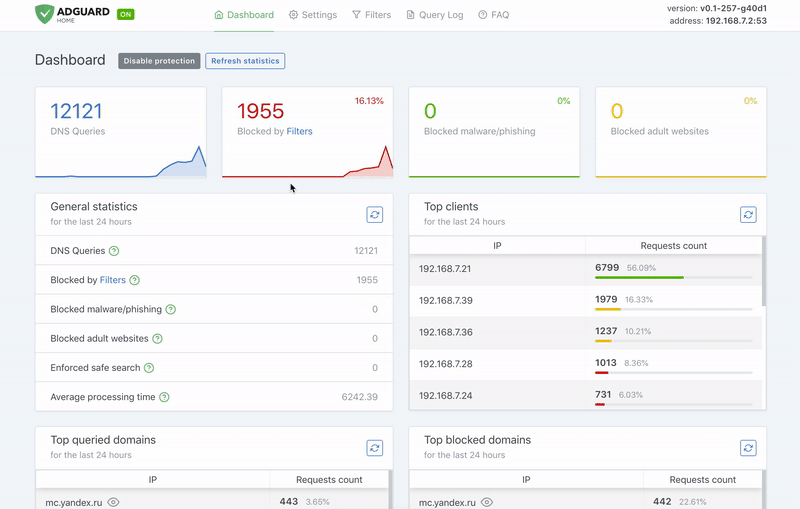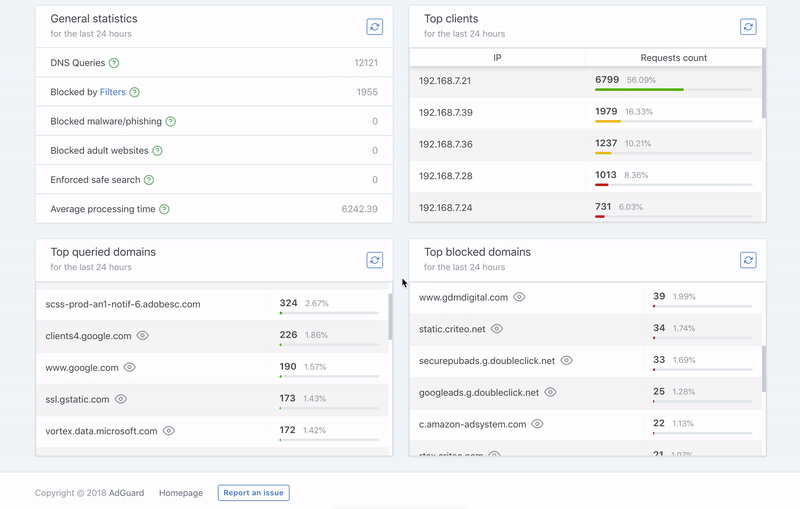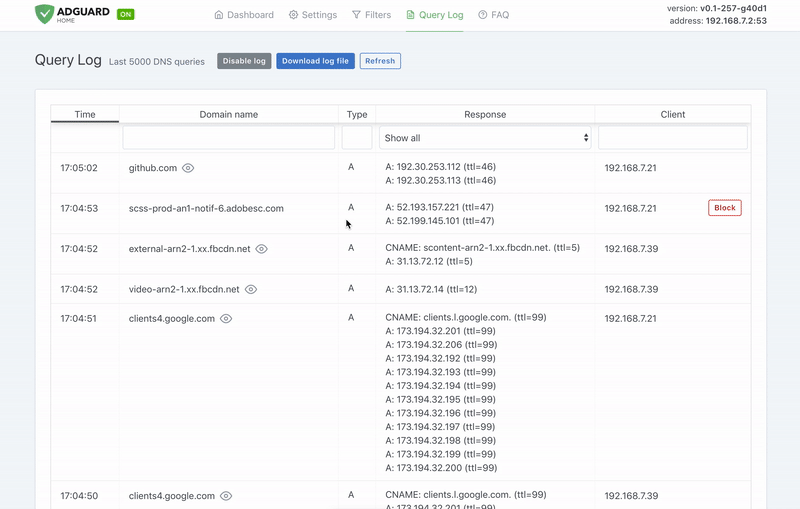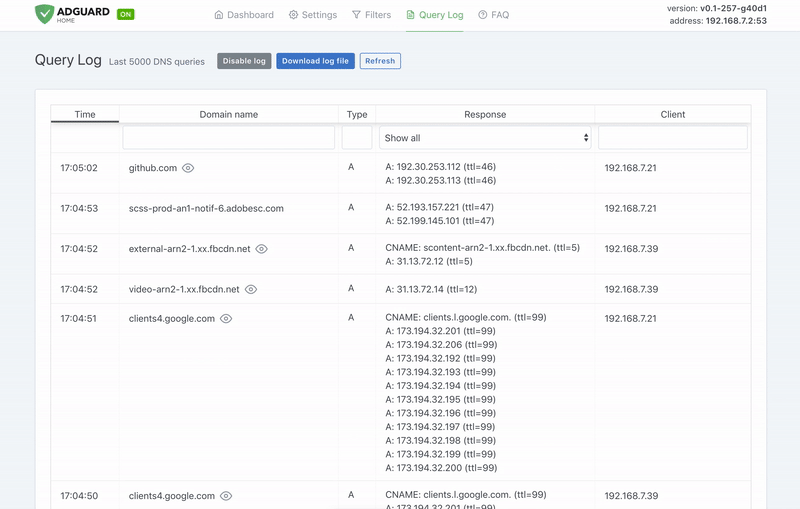
Featured Apps
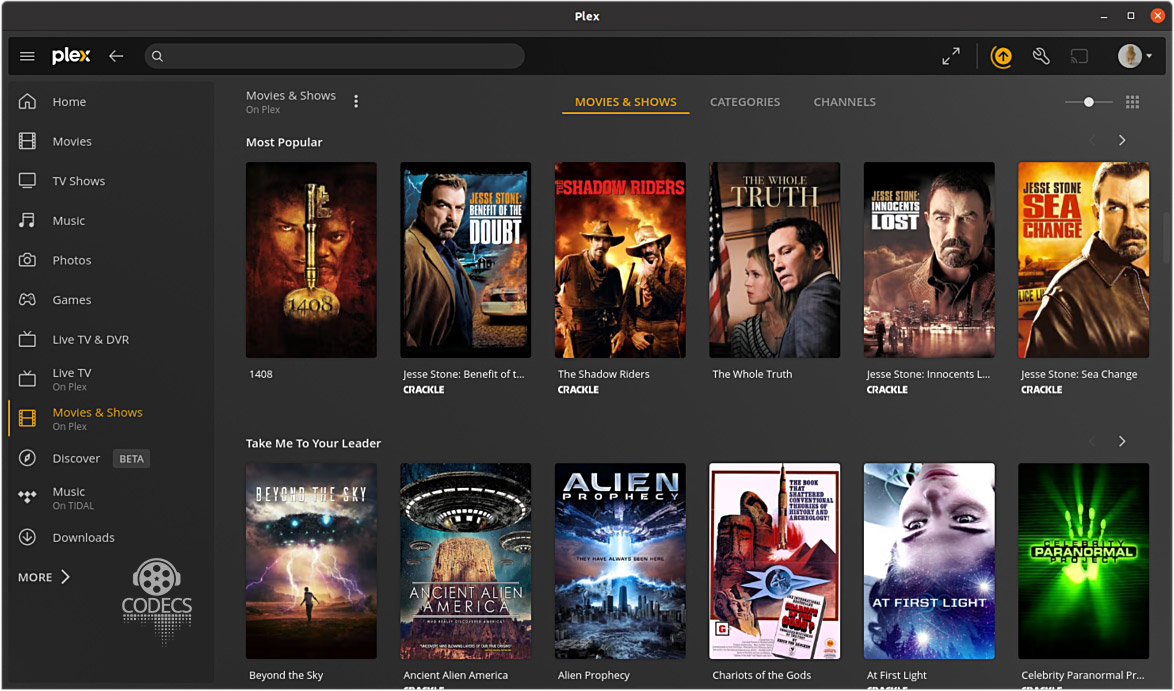
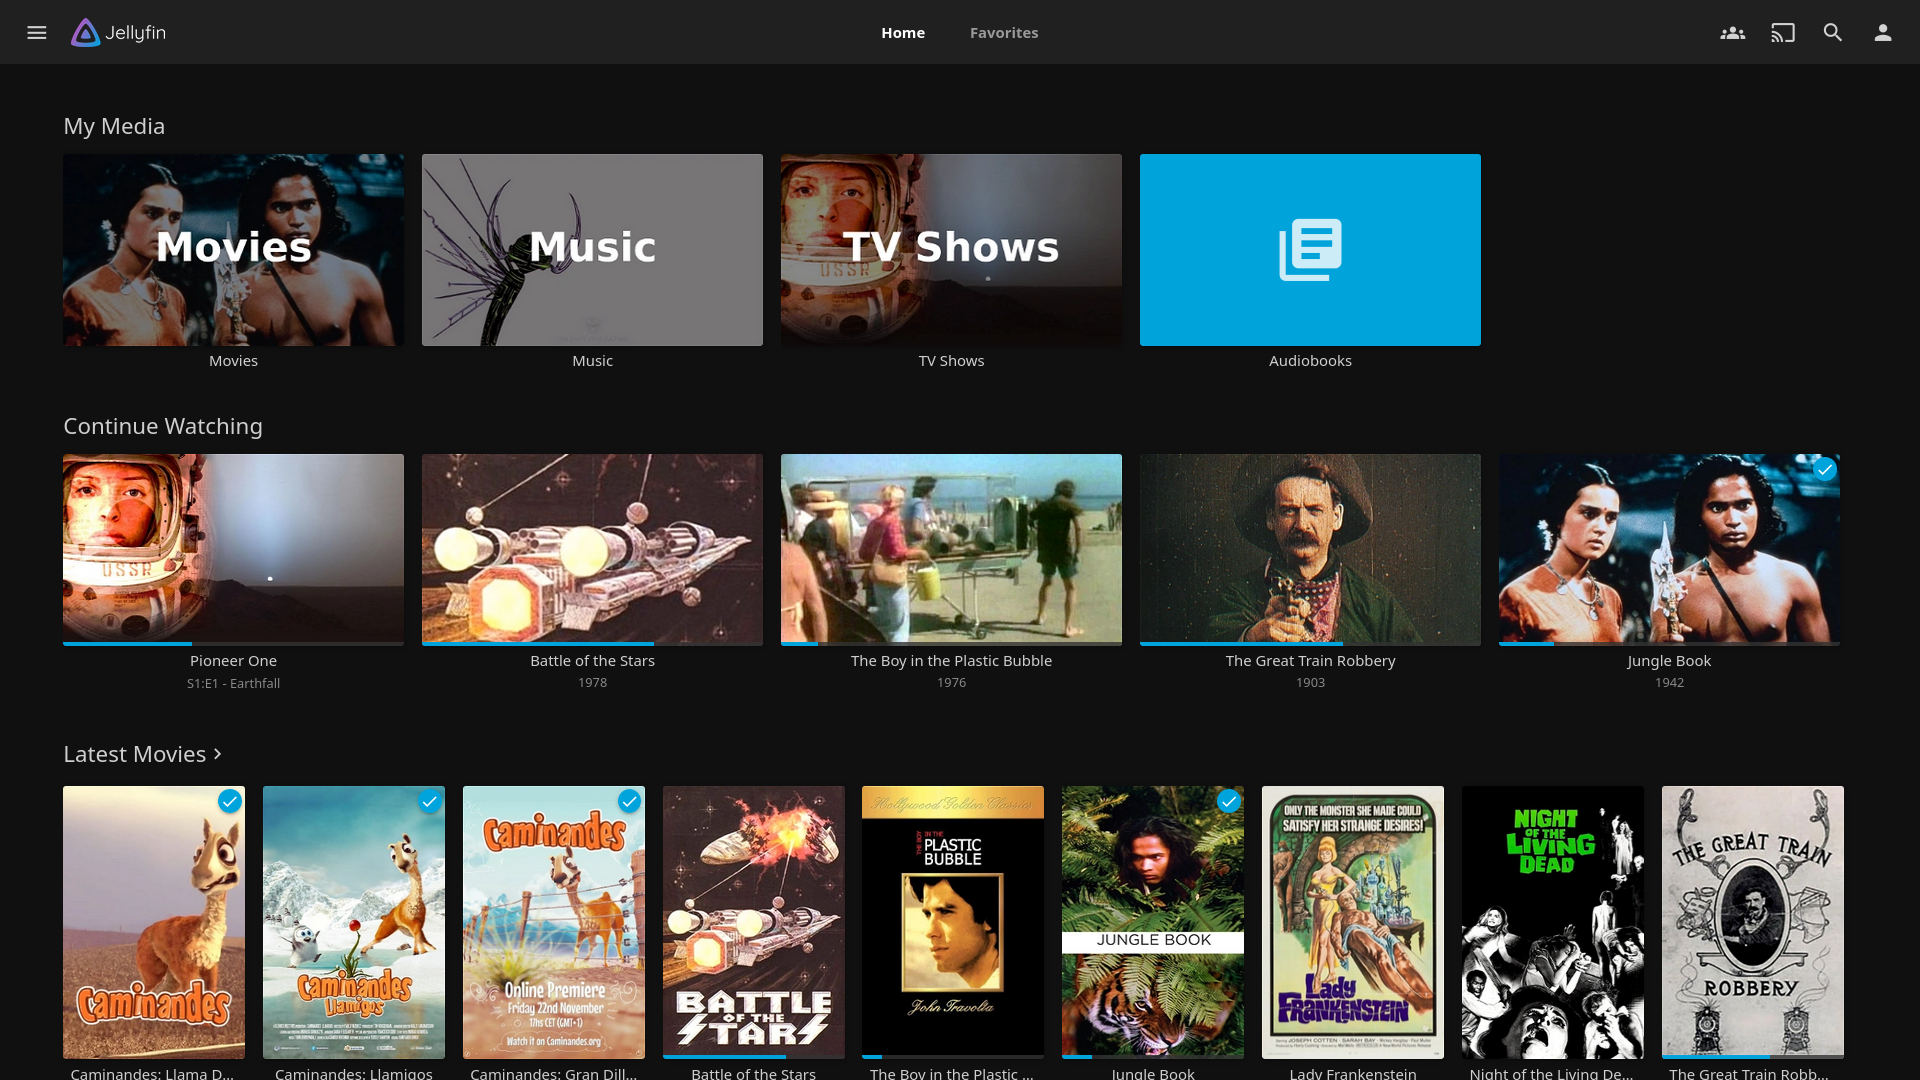


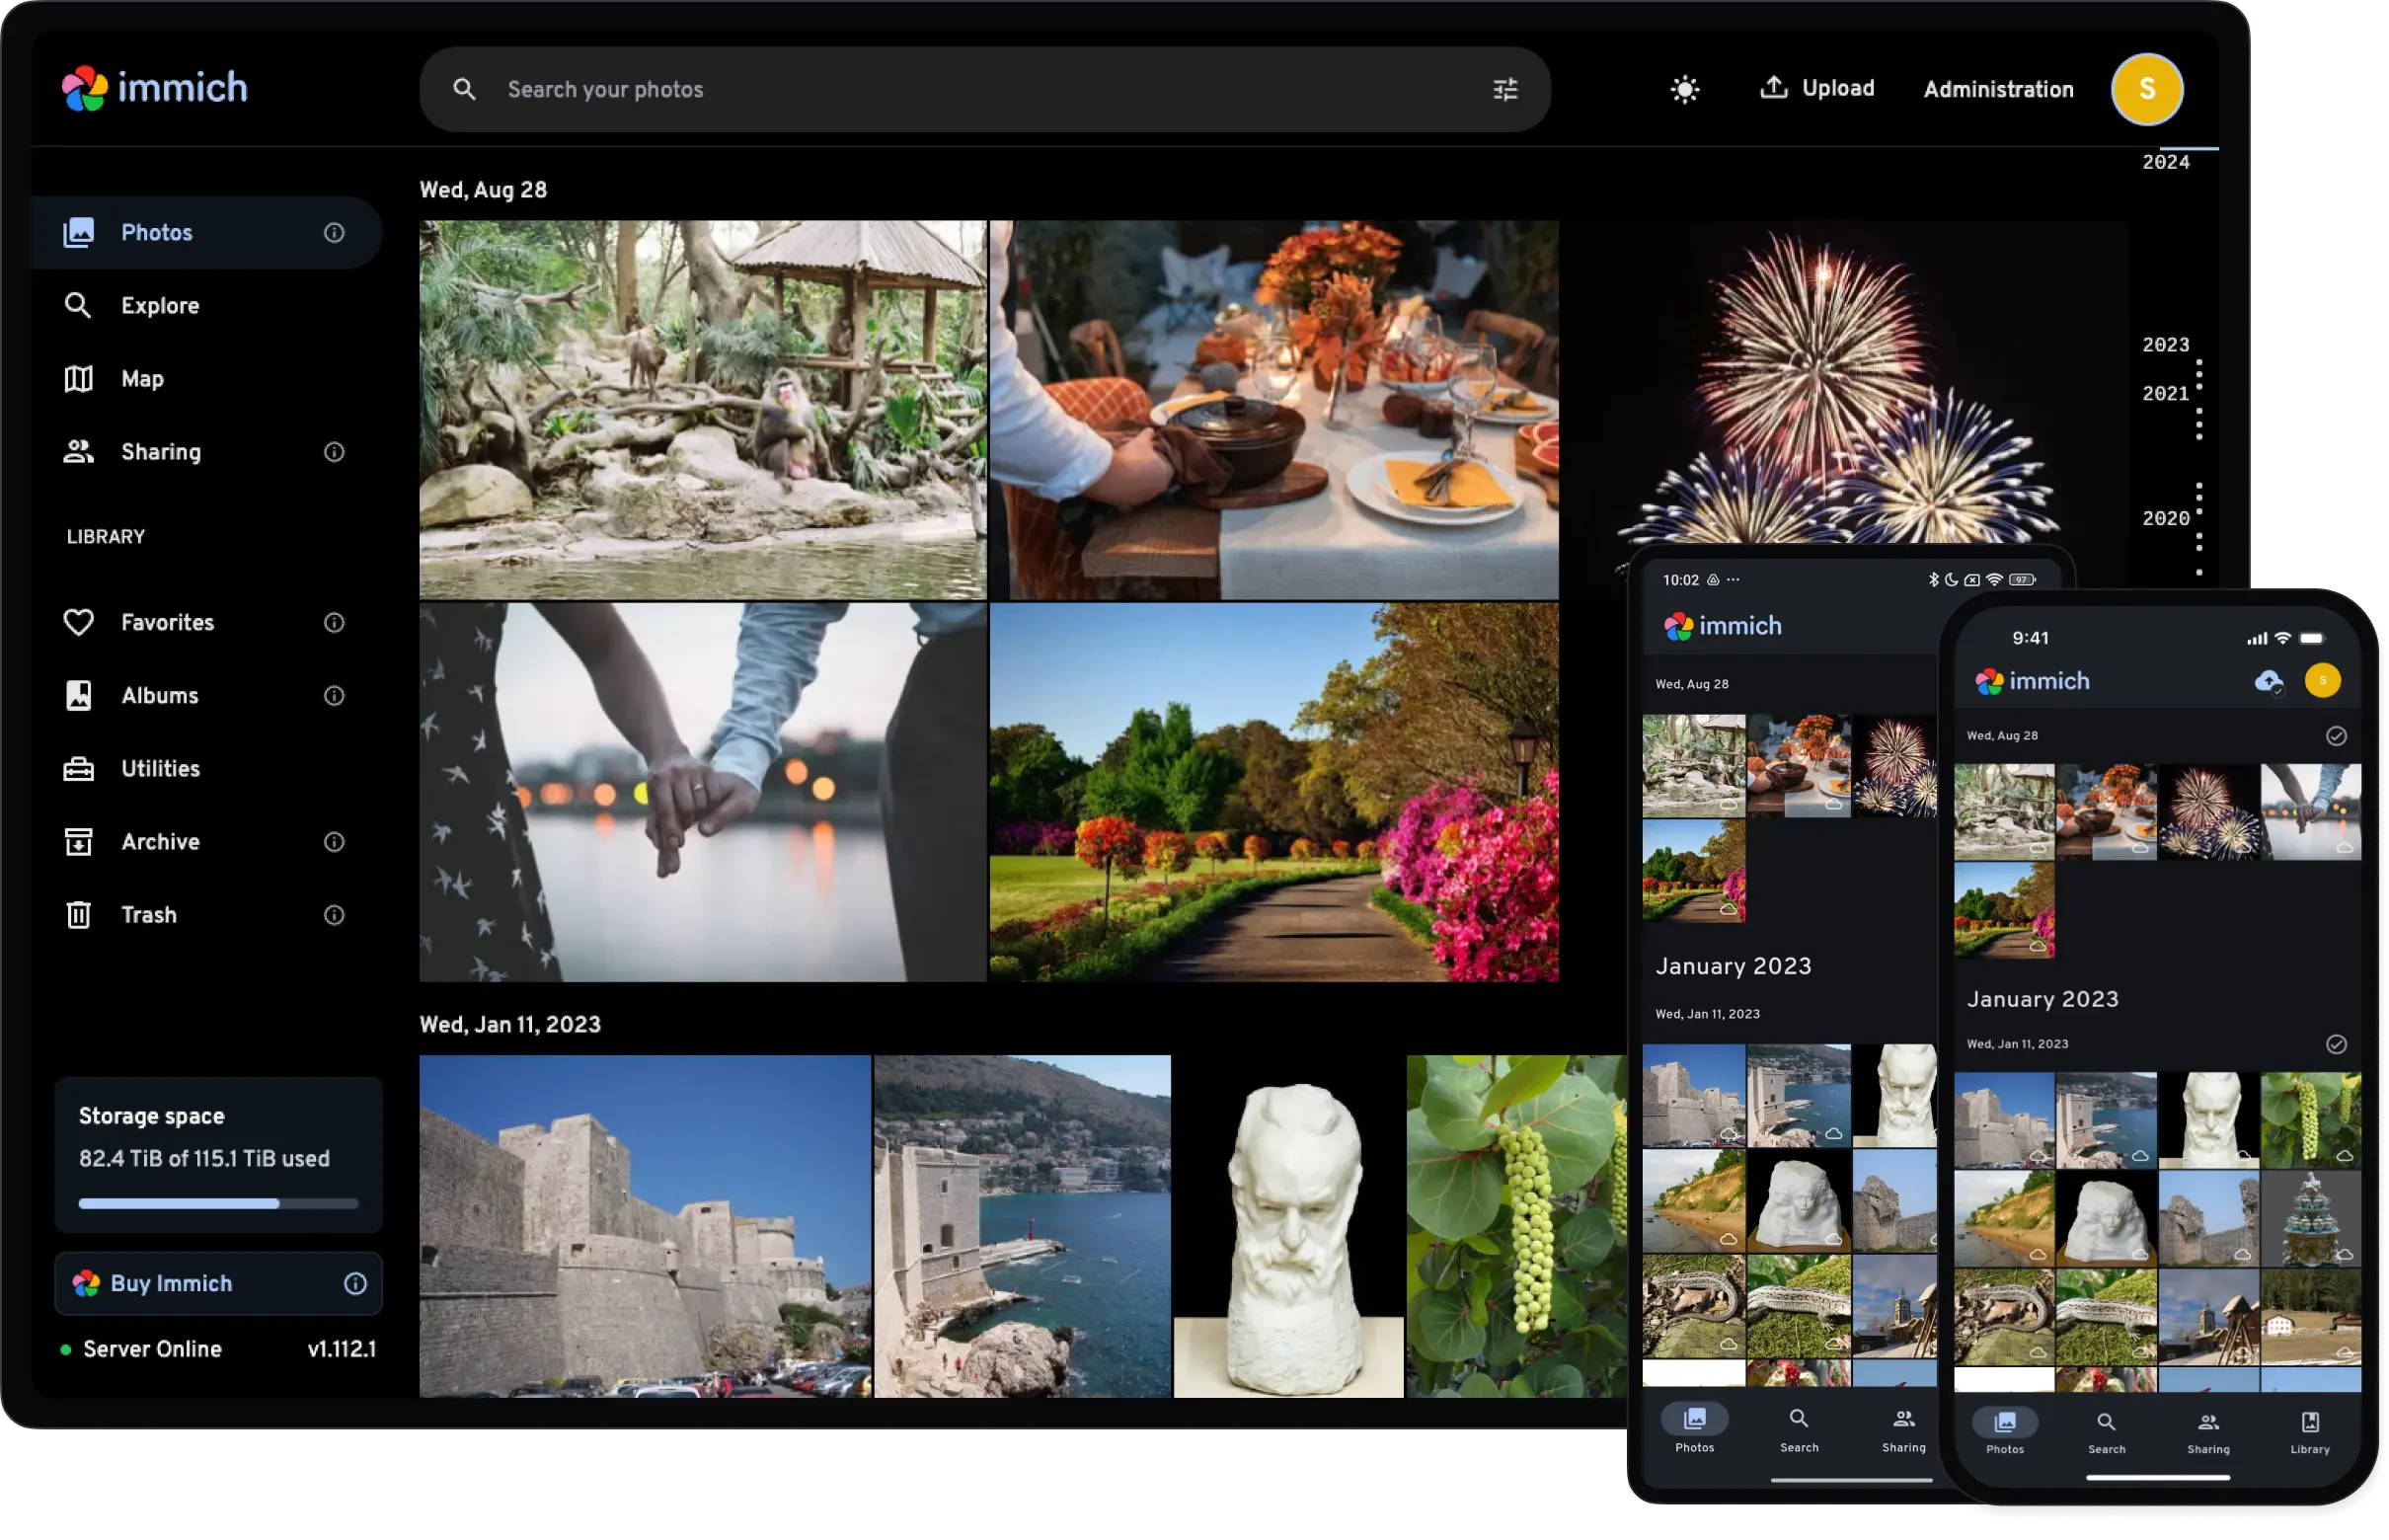
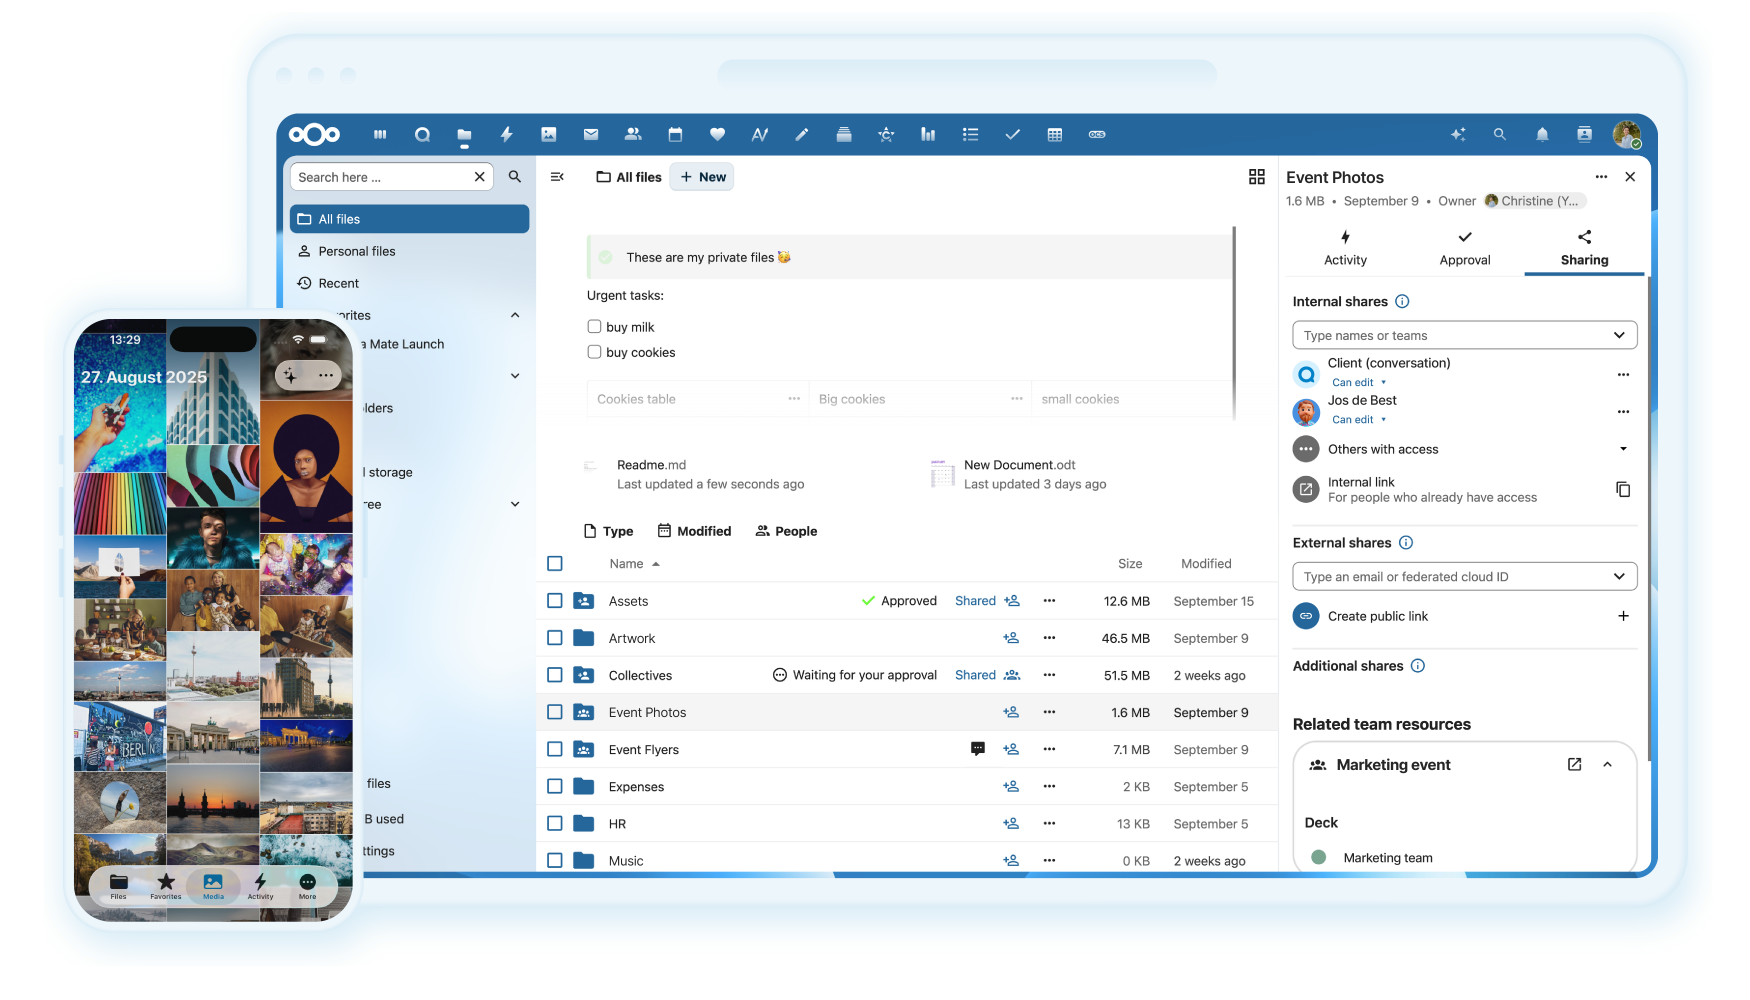

Positioning & Comparison
How Daemonless compares to traditional virtualization and manual jail administration.
| Feature | Docker on Linux/VM | Traditional Jails | Daemonless |
|---|---|---|---|
| OCI Images | Yes (Native) | No (Manual packages) | Yes (Standard OCI compliance) |
| Native FreeBSD | No (Requires Linux VM) | Yes (Native Jails) | Yes (Native Jails) |
| App-Store Deploy (Compose) | Yes (Docker Compose) | No (Custom shell/jails) | Yes (Podman/AppJail Compose) |
| VM Required | Yes (On non-Linux hosts) | No | No (Zero VM overhead) |
| ZFS Volume Integration | No (Virtual disk overhead) | Yes (Native datasets) | Yes (Native datasets) |
| In-Container Privilege | Varies by image | Manual (admin-configured) | Unprivileged by default (UID:GID 1000:1000) |
Host root is required to manage jails (same as Docker's own daemon on Linux) — that's independent of what runs inside one. See the security model breakdown for the full picture.
Architecture: How it Works
Run standard, unmodified container commands. Podman translates them natively to FreeBSD Jails.
flowchart TD
    host["FreeBSD Host Kernel"] --> runtime["Podman / ocijail / runj"]
    subgraph isolation["Native Jail Isolation (Zero VM Overhead)"]
        runtime --> base["Base Image (/init, rcd for appliances)"]
        base --> apps["Image Fleet (Plex, Radarr, Nextcloud...)"]
    end

    style host fill:#ab2b28,stroke:#333,stroke-width:2px,color:#fff
    style runtime fill:#2980b9,stroke:#333,stroke-width:2px,color:#fff
    style base fill:#d35400,stroke:#333,stroke-width:1px,color:#fff
style apps fill:#27ae60,stroke:#333,stroke-width:1px,color:#fff-
Reliable Foundation
Built on FreeBSD and native jails. The app is the container's process, so Podman, AppJail or Kubernetes restart, stop and log it like any other container. Appliances that bundle several services run them under
rcd(8). -
Minimal Footprint
Ultra-lightweight images with cleaned package caches and minimal overhead.
-
Secure by Default
Run as any user with PUID/PGID support. True isolation with Jails.
-
Networking
Full port forwarding support and seamless integration with
pffirewall. -
Automated Updates
Automated CI/CD pipelines ensure images are built against the latest upstream releases and FreeBSD packages.
-
Transparent & Open
100% open source. Every image is built from a visible
Containerfile.
Quick Example
Launch your first container in seconds with a familiar syntax.
PUID/PGID make Plex run as your own user, so its files on the host are yours. The host needs a few lines of pf first: see the Quick Start.
Ecosystem & Platforms
Run Daemonless images from the command line or through a FreeBSD management platform:
-
Podman & AppJail
Deploy directly with
podman-composeorappjail-directoron any FreeBSD 15 host. -
fjord
Lightweight web app store and Compose stack manager for FreeBSD (Podman & AppJail).
-
Sylve
Modern FreeBSD virtualization and system management platform for Bhyve VMs, Jails, ZFS, and Daemonless OCI containers.
-
FreeCORE
Community-driven FreeBSD and OpenZFS storage appliance carrying TrueNAS CORE forward, with native Daemonless container support.
Guides & How-Tos
-
Quick Start
Host setup,
pffirewall, and your first container — with Podman or AppJail. -
ZFS Storage
Map OCI volumes to native ZFS datasets for snapshots, quotas, and replication.
-
Networking
Port forwarding, bridges, and routing traffic behind a reverse proxy.
-
Operations & Updates
Keep services current with
podman pulland CI-rebuilt images — no manual jails.
Why Daemonless?
-
Philosophy
We believe in the power of FreeBSD Jails and the convenience of OCI containers. Daemonless is about bridging that gap for the community.
-
Architecture
Deep dive into how Podman, ocijail, and the FreeBSD kernel work together to provide native performance.
-
Join the Lab
Daemonless is more than a tool—it's a community of FreeBSD enthusiasts. Help us build the next generation of images.